AMLA Explained: What Europe's New Anti-Money Laundering Authority Changes
The EU’s new Anti-Money Laundering Authority, or AMLA, is designed to make enforcement more consistent across the single market. Its biggest near-term effect for most businesses will come from a unified AML rulebook, including more harmonised customer due diligence requirements.
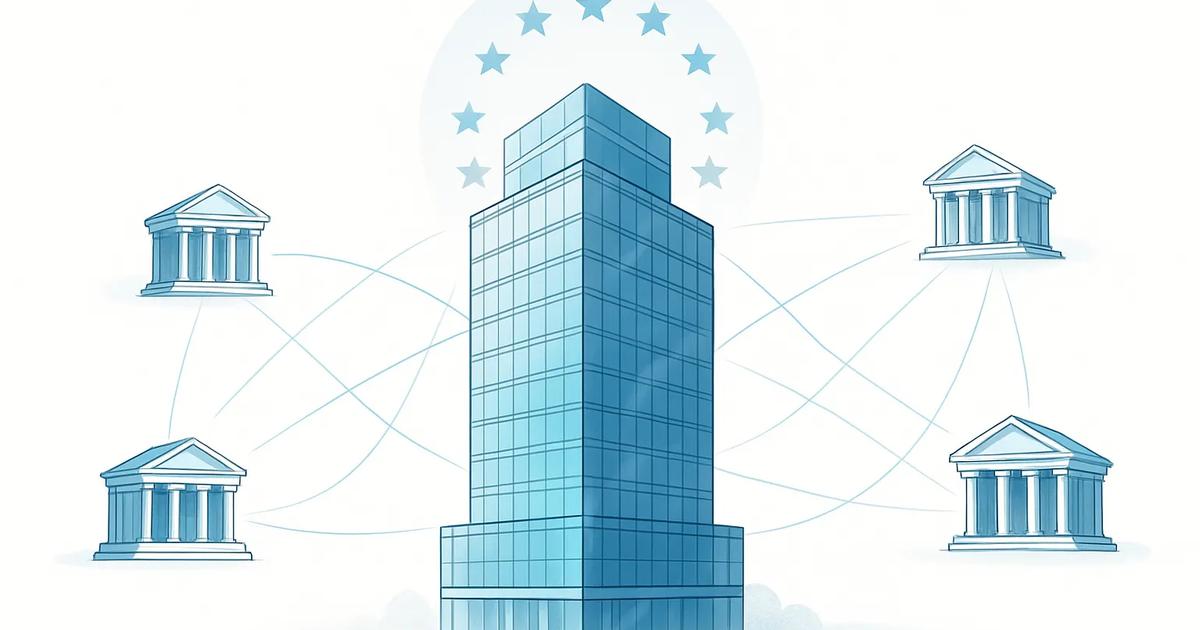
Europe’s new Anti-Money Laundering Authority, known as AMLA, is intended to close a longstanding gap in the EU’s financial-crime framework: rules have been set at EU level, but much of their implementation and supervision has remained national. Based in Frankfurt, AMLA was established under the EU’s 2024 anti-money laundering package and began building its operations in 2025.
The authority will not replace national regulators or turn every regulated business into an AMLA-supervised entity. Instead, it will sit at the centre of a new EU-wide system, coordinating national anti-money laundering supervisors and financial intelligence units, while directly overseeing a small group of higher-risk financial institutions that operate across borders. For identity verification providers and the firms that use them, the more immediate change is likely to be the single rulebook that underpins the new regime.
A shift from directives to a single rulebook
The 2024 package includes the Anti-Money Laundering Regulation, a directly applicable EU law. Unlike an EU directive, which each member state must transpose into domestic law, a regulation applies on the same legal basis across the bloc. The core rulebook is scheduled to apply from 2027, although implementation work and some related measures will continue beyond that point.
That distinction matters. Previous EU anti-money laundering directives set common objectives but left room for national choices in areas such as scope, thresholds, supervisory practice and the detailed application of customer due diligence. Customer due diligence, or CDD, is the process of identifying a customer, verifying their identity and, where relevant, understanding ownership, purpose and risk before or during a business relationship.
National laws will still matter, particularly for enforcement, sanctions and areas that remain outside the regulation’s full harmonisation. But the new approach should reduce the extent to which a bank, payments firm, crypto-asset business or other obliged entity must design separate onboarding and monitoring processes for each EU market.
What AMLA will do
AMLA’s mandate combines supervisory coordination, direct supervision in selected cases and support for cooperation among financial intelligence units. Financial intelligence units, often called FIUs, receive and analyse suspicious transaction reports and share intelligence with relevant authorities. Their effectiveness can depend on rapid cross-border information exchange, especially where customers, transactions and corporate structures span several jurisdictions.
The authority is expected to promote more consistent supervisory methods among national authorities, help address weaknesses in cross-border cases and develop common approaches under the new legal framework. It will also have a role in improving cooperation between FIUs and supporting EU-level analysis of money-laundering and terrorist-financing risks.
From 2028, AMLA is expected to directly supervise a limited set of high-risk financial institutions with substantial cross-border activity. The precise population will be determined under the framework’s selection process and can change over time. Direct supervision is therefore important symbolically and operationally, but it will apply to a narrow share of the market. Most firms will continue to deal primarily with their national supervisor.
Why identity verification teams should pay attention
For onboarding teams, the central promise is greater consistency in CDD expectations. A firm serving customers in several member states should face fewer jurisdiction-specific interpretations of baseline identification and verification obligations. That could simplify product design, control testing, vendor governance and audit preparation.
Harmonisation does not mean that every customer journey will become identical. Risk-based controls remain fundamental to EU AML law. Businesses will still need to determine when standard checks are sufficient, when enhanced due diligence is required, and how to handle legal-entity ownership, politically exposed persons, suspicious activity and higher-risk geographies. Data-protection rules, sector-specific requirements and national enforcement practice will also continue to shape implementation.
- Map current customer due diligence flows against the forthcoming EU-wide requirements and identify country-specific deviations.
- Review how identity evidence, liveness checks, document verification, beneficial-ownership data and screening results are recorded and retained.
- Assess whether third-party identity verification providers can support consistent controls, audit evidence and changes to regulatory guidance.
- Keep governance flexible: detailed technical standards, supervisory expectations and national implementation arrangements will continue to develop before 2027.
The practical impact will arrive before direct supervision
Businesses should not assume AMLA is relevant only if they may be selected for direct oversight. For most obliged entities, the single rulebook will be the more consequential development. It changes the compliance baseline against which national supervisors will assess customer onboarding, ongoing monitoring and internal controls.
Preparation is also not simply a legal exercise. Firms with fragmented EU operations may need to reconcile customer-risk models, data fields, escalation processes and evidence standards. Identity verification systems will need to support both a more common EU baseline and the ability to document risk-based decisions. In practice, that means compliance, product, fraud, data-protection and procurement teams will all have a role.
A more coherent system, not a uniform outcome overnight
AMLA is a significant institutional change, but its success will depend on staffing, cooperation with national authorities and the quality of the technical rules that follow. A directly applicable regulation can reduce legal fragmentation, yet supervisory convergence takes time and will be tested by differing national risk profiles and enforcement traditions.
The direction of travel is nonetheless clear. The EU is moving from a framework built largely on national transposition toward a more centralised and consistent anti-money laundering architecture. Companies onboarding EU customers should treat 2027 as an implementation milestone, while recognising that AMLA’s influence on supervision and cross-border coordination will continue to grow after that date.