Transaction Monitoring: Why Most Alerts Are False
Transaction monitoring is central to anti-money-laundering compliance, yet its alerts are often noise. The challenge for banks is to detect genuinely suspicious activity without overwhelming investigators or missing the cases that matter.
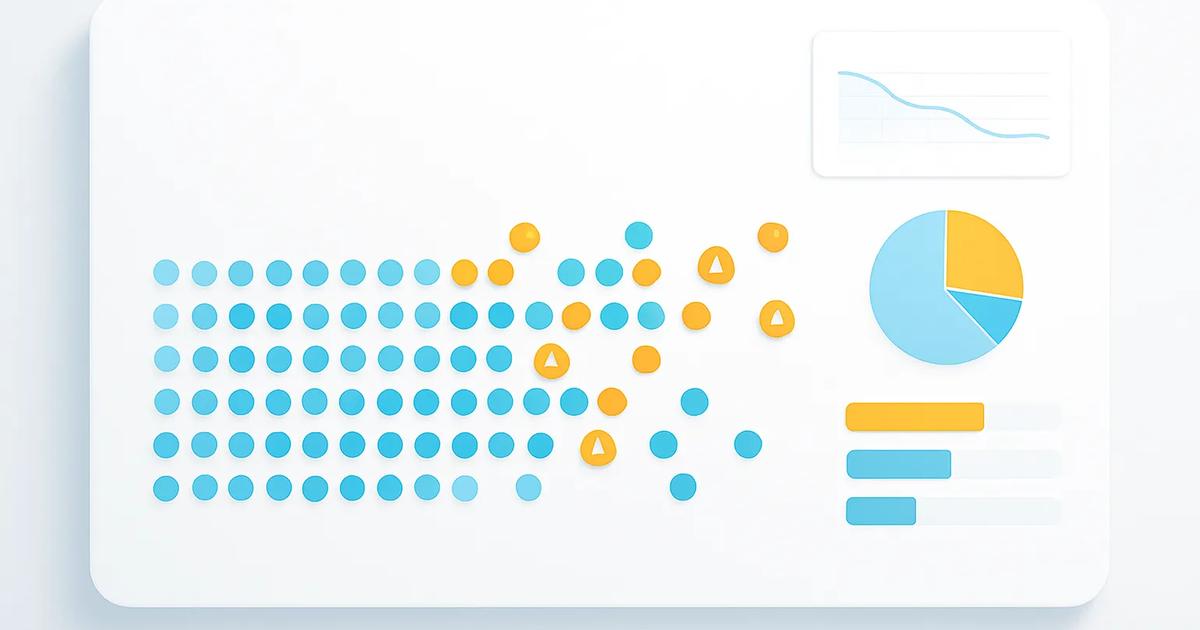
Transaction monitoring has a paradox at its center. Banks must scan vast volumes of payments for possible money laundering, fraud and sanctions evasion, but the rules designed to surface risk commonly generate alerts that do not become reportable cases. The result is a costly queue of reviews, where investigators spend time clearing ordinary customer behavior while consequential activity can sit unresolved.
For US and European supervisors, the question is increasingly not whether a firm has a monitoring system. It is whether its scenarios, thresholds, customer risk ratings and investigative capacity are calibrated to the business it actually conducts. That focus has sharpened as banks move from overnight processing to systems that assess transactions as they are initiated or settled.
Why a rule becomes an alert
Rules-based monitoring compares transactions with preset conditions. A rule might flag a cash transaction above a reporting threshold, a sudden payment to a high-risk jurisdiction, or movement of funds inconsistent with a customer's expected activity. It is straightforward to audit and explain, but it is necessarily blunt: a legitimate customer can look unusual, while a sophisticated criminal can structure activity to appear routine.
In the United States, financial institutions generally must file a Currency Transaction Report for cash transactions exceeding $10,000 in one business day. Structuring, the deliberate breaking up of transactions to avoid that requirement, may appear as repeated cash deposits just below the threshold. FinCEN guidance also identifies rapid movement of funds, deposits followed by immediate withdrawals, and transfers involving higher-risk jurisdictions as potential red flags. None is proof of wrongdoing. Each requires context.
- A newly opened account receives several large third-party credits and sends them onward within hours.
- Cash is deposited in amounts just under reporting thresholds across branches or days.
- A customer with a local retail profile begins sending payments to jurisdictions subject to elevated Financial Action Task Force scrutiny.
- A payment pattern conflicts with known income, business purpose or prior account behavior.
Jurisdiction risk is not static. The Financial Action Task Force, or FATF, updates its public lists following plenary meetings, so monitoring teams must refresh country logic and assess what the changes mean for their own exposure. A country reference alone should not decide an alert outcome, particularly where customers have legitimate cross-border ties.
The cost of noise, and the cost of getting it wrong
False positives are not merely an efficiency problem. Large alert volumes can create backlogs, reduce the time available for complex investigations and make it harder for senior compliance staff to identify deterioration in controls. At the other extreme, reducing alerts too aggressively can leave suspicious activity undetected or unreported.
Vendor materials frequently claim that real-time monitoring can reduce fraud losses by 60% to 80%, or cut false positives by 40% to 60%. Those are marketing claims, not industry-wide benchmarks. Results depend on payment type, data quality, the baseline rules being replaced, the definition of a false positive, and whether a firm measures prevented losses or alerts closed without escalation. Buyers should ask for independently verifiable methodology and comparable before-and-after measures.
TD Bank made the operational stakes plain
The enforcement action against TD Bank illustrates why staffing, governance and alert handling matter as much as detection software. On 10 October 2024, FinCEN assessed TD Bank a $1.3 billion civil money penalty, the largest penalty against a depository institution in FinCEN history. The action was part of a wider US resolution and required a four-year independent monitorship.
FinCEN said TD Bank operated an under-resourced anti-money-laundering programme, failed to sufficiently monitor peer-to-peer transactions conducted through Venmo and Zelle, and accumulated a backlog of suspicious-activity reviews. Its findings also included willful failure to file Suspicious Activity Reports, or SARs, involving roughly $1.5 billion in transactions. Source: FinCEN, “FinCEN Assesses $1.3 Billion Penalty Against TD Bank,” 10 October 2024.
The case does not establish that every high-alert environment is deficient. It does show regulators examining whether institutions have matched controls and people to their transaction volumes, products and risk. A system that generates alerts faster than a bank can investigate them is not delivering an effective control simply because it is technically operating.
From batch review to real-time decisions
Historically, many monitoring platforms processed data in end-of-day batches. That model can identify suspicious patterns after funds have moved, but it is less useful where a bank needs to hold, step up authentication for, or quickly review a payment. Real-time monitoring aims to score activity during the payment flow, combining transaction details with customer, device, counterparty and behavioral data where permitted.
Machine learning can help rank alerts and identify patterns that fixed rules miss, but it does not remove the need for accountable design. Models can reproduce poor data, become less accurate as customer behavior changes, and be difficult to explain to investigators and supervisors. Effective programmes keep clear audit trails, test outcomes, tune thresholds against confirmed cases and ensure human reviewers can challenge automated results.
A long-running compliance problem
The US Bank Secrecy Act dates to 1970 and established core recordkeeping and currency-reporting duties that underpin modern financial-crime controls. Formal SAR requirements developed later through 1990s legislation and regulation. FATF was established in 1989 and has since set influential global standards for anti-money-laundering and counter-terrorist-financing controls.
That history explains why monitoring remains rule-heavy, but the direction of travel is clear. Supervisors are asking for evidence that a bank understands the risks in its own data, can explain how its controls are tuned, and can turn alerts into timely decisions. The goal is not the fewest alerts. It is a defensible system that finds the right ones.