KYC Automation: What Can Be Automated and What Still Needs People
KYC automation can speed routine customer due diligence, but it does not remove a regulated firm’s responsibility to understand risk. The most effective programs automate repeatable checks and route ambiguous or high-risk cases to trained reviewers.
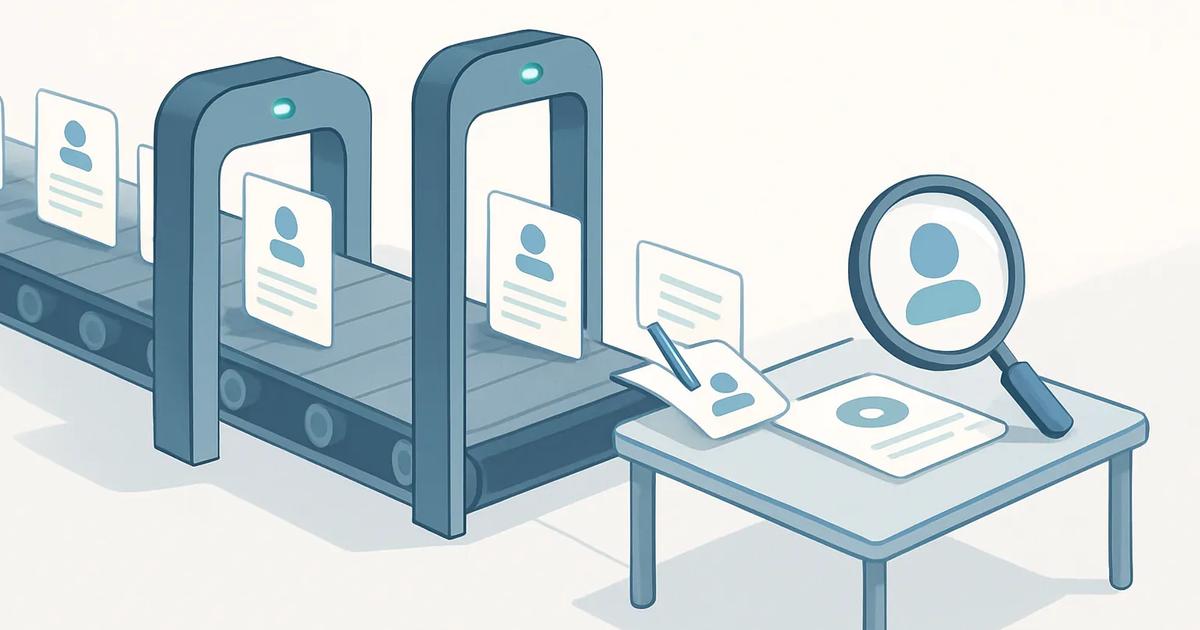
Know your customer, or KYC, automation is the use of software to complete customer due diligence steps with little or no manual handling. Customer due diligence is the process financial institutions and other regulated businesses use to identify customers, verify their identities, assess risk and monitor relationships over time.
Automation can reduce rekeying, shorten onboarding and make screening more consistent. It is not a substitute for accountability. In the United States, firms remain responsible for meeting Bank Secrecy Act and anti-money laundering obligations. In the European Union, obliged entities must meet requirements under the EU anti-money laundering framework and applicable national rules. Software can support those duties, but the firm must govern its use and act on the results.
What KYC automation does well
The strongest use cases are structured, repeatable tasks where systems can apply defined rules, compare reliable sources and preserve a record of each action. Automation is especially useful at the start of a customer relationship, but can also support ongoing monitoring.
- Data capture and validation: Optical character recognition can extract names, dates of birth, addresses and document numbers from identity documents. Software can check formatting, detect missing fields and compare entered information with the document image.
- Document and biometric checks: Tools can assess document security features, detect signs of alteration and test whether a document image is likely genuine. A selfie or short video can be compared with the portrait on an identity document through biometric matching and liveness detection, which is intended to determine whether a real person is present rather than a photo, replayed video or mask.
- Business registry lookups: For legal-entity customers, systems can retrieve company registration details from official or commercial registries, where available. They can collect directors, registered addresses and, in some jurisdictions, beneficial ownership data. A beneficial owner is the person who ultimately owns or controls a company.
- Sanctions and PEP screening: Screening engines compare customer and associated-party data against sanctions lists, politically exposed person, or PEP, data, and adverse-media sources. A PEP is an individual entrusted with a prominent public function and may require greater scrutiny because of corruption risk.
- Risk scoring: Rules and statistical models can assign an initial risk rating using factors such as country exposure, product type, expected activity, ownership characteristics and screening results. The score can determine which cases proceed automatically and which are reviewed.
- Event-driven refresh: Rather than updating every file only on a fixed schedule, systems can trigger a review when a sanctions list changes, an ownership record changes, an identity document expires or customer activity departs from an expected pattern.
Where people remain essential
Automated checks produce signals, not final truth. Data sources can be incomplete, names can be transliterated in several ways, and a technically valid document does not establish the purpose of a relationship. Human review is most valuable where evidence conflicts, the risk is elevated or the firm must make a contextual judgement.
Complex ownership and control
Corporate ownership can involve multiple entities, trusts, nominees, partnerships and companies in several jurisdictions. Software can map known relationships, but investigators may need to reconcile conflicting registry records, obtain source documents and determine who actually exercises control. This work is central to identifying beneficial owners and cannot safely be reduced to a simple percentage calculation in every case.
True-match investigations and enhanced due diligence
A screening alert is not necessarily a match. Reviewers must decide whether a customer is the same person named on a sanctions list, PEP record or adverse-media report. That assessment can require dates of birth, nationality, location, employment history and source reliability. For higher-risk relationships, enhanced due diligence may require judgement about source of funds, source of wealth, the customer’s business rationale and the adequacy of mitigating controls.
Suspicious activity decisions
Transaction-monitoring systems can identify unusual patterns, but they do not decide whether activity is suspicious. Investigators consider the customer profile, transaction context, available explanations and relevant evidence. In the US, a covered financial institution may need to file a suspicious activity report. EU reporting terminology and procedures vary by member state, but suspicious transaction reports are generally made to the relevant financial intelligence unit. These are consequential legal decisions that require accountable human oversight.
How to read straight-through processing rates
Straight-through processing, often shortened to STP, measures the proportion of onboarding applications completed without a human reviewer. Firms commonly calculate it as automated approvals divided by all completed or eligible applications over a defined period. They may also track automated declines, referrals to review, abandonment and the reasons cases left the automated path.
A rising STP rate can indicate that data capture and decision rules are working efficiently. It is not, by itself, evidence of a stronger compliance program. If thresholds are loosened merely to reduce referrals, the system may approve customers with unresolved identity, sanctions or fraud signals. Firms should set risk-based routing rules, test outcomes against later findings and monitor whether automated decisions vary unexpectedly across customer groups, products or geographies.
Audit trails and explainable decisions
Regulators, auditors and internal compliance teams need to reconstruct how a decision was reached. An adequate audit trail records the data received, source checks performed, list versions used, rules or model outputs applied, alerts generated, reviewer actions, overrides and the final decision. It should also show when the decision occurred and which policy was in force.
Explainability does not require every tool to expose its proprietary code. It does require a firm to explain, in practical terms, why an application was approved, declined or referred. For model-based tools, firms should understand input data, performance limits, escalation criteria and material sources of error. They should validate vendors, test changes before deployment, control access to sensitive identity data and retain records for the periods required by applicable law.
The durable model is not fully automated KYC. It is controlled automation: machines handle high-volume evidence gathering and consistent checks, while people make accountable decisions when risk or ambiguity demands judgement.
The operating principle
KYC automation works best when it is designed as a triage and evidence-management system rather than an autonomous compliance function. Firms should automate clear, low-risk tasks; maintain defined human escalation paths; and regularly review false positives, false negatives and customer outcomes. That approach can improve speed without treating efficiency as a reason to lower the standard of due diligence.